 Secure Desk
Which option should I choose?
The supported machine always runs the native Windows client — a web page can't inject operating-system mouse and keyboard input. What varies is whether that client is installed.
Attended Support
Help someone while they're at their computer.
- No permanent installation
- No administrator rights needed
- User starts the connection
- Session ends when the client closes
Unattended Access
Connect to your devices, even when nobody is there.
- One-time installation
- Persistent device access
- Access before a user signs in
- Background troubleshooting tools
Attended support — start a one-time session
Create a support session
Sign in to your portal, open Support, and create a session with a label, an expiry, one-time or reusable, and private (code/link) or public listing.
Share the connection link
Send the session link or code to the person who needs help.
The user opens Secure Desk
They download and launch the small portable connector. It runs in their own session, needs no admin rights and installs nothing.
Connect and provide support
Open the session in your browser console, confirm the 6-digit code, and help.
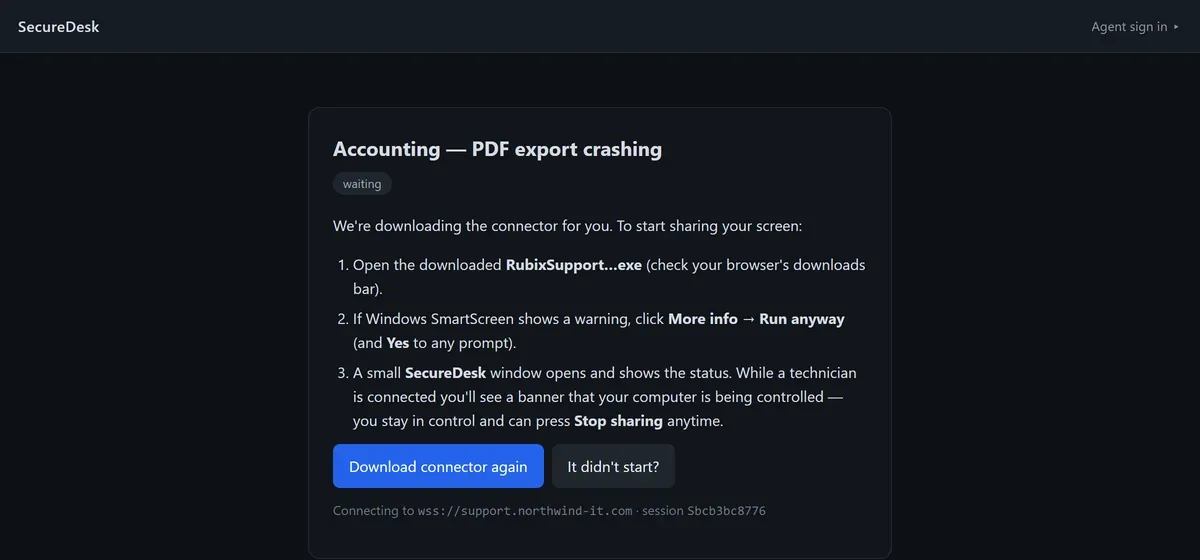
Temporary access. The portable client runs only for the support session. Closing it ends the connection. Public sessions appear on the join page by name — anyone who can reach it can join without a code, so keep sensitive sessions private.
Administrator access & elevation
A standard-user session can't fix a service or a driver. The technician clicks Elevate and enters that machine's own administrator account; the client relaunches itself with those rights via a linked-token launch and reports the integrity level it actually obtained.
- Credentials are used once on that machine, never persisted, never logged, and never reach the portal.
- The console refuses to send them unless the session is end-to-end encrypted — verify the 6-digit code first.
- Prefer short-lived, dedicated support-admin accounts, and log every escalation.
- On the portable client, elevation is best-effort and depends on UAC policy. The installed service is the robust route to full rights.
Unattended access — set up ongoing access
Install the Windows client
Install the Secure Desk service from an elevated PowerShell prompt. It runs as LocalSystem from boot.
Enroll the device
The device enrolls with your portal, carries its own device token, and appears in your per-customer device inventory.
Find your computer
Open the device inventory in your portal and select the computer you want to support.
Connect whenever needed
Start a session — including when nobody is signed in. The service survives logon, lock and fast user switching.
Administrator permissions required. Installing the Windows service requires elevated permissions. Once enrolled, the device can be accessed by technicians with the appropriate permissions.
In normal use you don't hand-write session ids: the device enrolls with the portal and carries its own device token. A technician with the devices.connect permission opens a session against it directly.
Sign-in screens & display limitations
A Windows service runs in Session 0, isolated from the desktop, so the service spawns its capture worker in the active console session and relaunches it across session changes. On the sign-in desktop, Secure Desk switches to DXGI Desktop Duplication when it's available, falling back to GDI otherwise (with the reason recorded in diagnostics).
The secure desktop is not captured: UAC consent prompts and Ctrl+Alt+Del run on a separate, protected desktop. Backstage already works before login because it needs no desktop at all.
Backstage — a SYSTEM shell with no desktop
The installed service also exposes backstage: cmd or PowerShell running as SYSTEM with no interactive desktop. Technicians can run privileged commands and move files without disturbing the user's screen, and it works when nobody is signed in. The portable client never starts one.
Treat backstage as handing out a remote SYSTEM command prompt. Portal roles don't isolate backstage per technician, and backstage commands aren't logged. The Business audit log keeps the last 200 administrative and session events — not command-level shell activity.
Tools in every session
Screen & control
View and interact with remote Windows desktops.
Multiple monitors
Switch between connected displays.
File transfer
Send and receive files, SHA-256 verified.
Clipboard
Two-way text sync, on request.
Voice
16 kHz audio over the same encrypted channel, optional technician webcam.
Background tools
Backstage SYSTEM shell (installed service).
Next: licensing & updates
Activate your plan and learn how Secure Desk stays up to date.
Something unclear or missing? Tell us and we'll improve this page.